SC-401 Sample Practice Exam Questions 2025 Updated Verified [Q33-Q50]

5/5 - (4 votes)

SC-401 Sample Practice Exam Questions 2025 Updated Verified

Exam Study Guide Free Practice Test LAST UPDATED SC-401

Microsoft SC-401 Exam Syllabus Topics:

Topic Details
Topic 1
  • Implement Information Protection: This section measures the skills of Information Security Analysts in classifying and protecting data. It covers identifying and managing sensitive information, creating and applying sensitivity labels, and implementing protection for Windows, file shares, and Exchange. Candidates must also configure document fingerprinting, trainable classifiers, and encryption strategies using Microsoft Purview.
Topic 2
  • Implement Data Loss Prevention and Retention: This section evaluates Data Protection Officers on designing and managing data loss prevention (DLP) policies and retention strategies. It includes setting policies for data security, configuring Endpoint DLP, and managing retention labels and policies. Candidates must understand adaptive scopes, policy precedence, and data recovery within Microsoft 365.
Topic 3
  • Protect Data Used by AI Services: This section evaluates AI Governance Specialists on securing data in AI-driven environments. It includes implementing controls for Microsoft Purview, configuring Data Security Posture Management (DSPM) for AI, and monitoring AI-related security risks to ensure compliance and protection.
Topic 4
  • Manage Risks, Alerts, and Activities: This section assesses Security Operations Analysts on insider risk management, monitoring alerts, and investigating security activities. It covers configuring risk policies, handling forensic evidence, and responding to alerts using Microsoft Purview and Defender tools. Candidates must also analyze audit logs and manage security workflows.


Q33. You have a Microsoft 365 subscription.
You have a user named User1 Several users have full access to the mailbox of User1.
Some email messages sent to User 1 appeal to have been read and deleted before the user viewed them When you search the audit log in the Microsoft Purview portal to identify who signed in to the mailbox of User l. the results are blank.
You need to ensure that you can view future sign-ins to the mailbox of User1.
Solution: You run the Set-AuditConfig -Workload Exchange command.
Does that meet the goal?


Q34. You have a Microsoft 365 E5 subscription that has data loss prevention (DLP) implemented.
You plan to export DLP activity by using Activity explorer.
The exported file needs to display the sensitive info type detected for each DLP rule match.
What should you do in Activity explorer before exporting the data, and in which file format is the file exported? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q35. You have a Microsoft 365 tenant.
You have a database that stores customer details. Each customer has a unique 13-digit identifier that consists of a fixed pattern of numbers and letters.
You need to implement a data loss prevention (DLP) solution that meets the following requirements:
*Email messages that contain a single customer identifier can be sent outside your company.
*Email messages that contain two or more customer identifiers must be approved by the company’s data privacy team.
Which two components should you include in the solution? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.


Q36. HOTSPOT
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.

You plan to create a Microsoft Purview insider risk management case named Case1.
Which insider risk management object should you select first, and which users will be added as contributors for Case1 by default?
To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q37. You need to meet the technical requirements for the creation of the sensitivity labels.
To which user or users must you assign the Sensitivity Label Administrator role?


Q38. You are creating a data loss prevention (DLP) policy that will apply to all available locations except Fabric and Power BI workspaces.
You configure an advanced DLP rule in the policy.
Which type of condition can you use in the rule?


Q39. You have a Microsoft 365 E5 subscription.
You need to ensure that encrypted email messages sent to an external recipient can be revoked or will expire within seven days.
What should you configure first?


Q40. You have a Microsoft 365 subscription. Auditing is enabled.
A user named User1 is a member of a dynamic security group named Group1.
You discover that User1 is no longer a member of Group1.
You need to search the audit log to identify why User1 was removed from Group1.
Which two activities should you use in the search? To answer, select the appropriate activities in the answer area.
NOTE: Each correct selection is worth one point.

Q41. HOTSPOT
You have a Microsoft 365 E5 subscription.
You receive the data loss prevention (DLP) alert shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

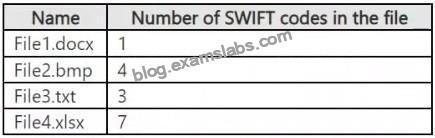
Q42. You have a Microsoft SharePoint Online site that contains the following files.

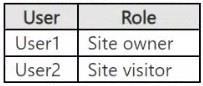
Users are assigned roles for the site as shown in the following table.

Which files can User1 and User2 open? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

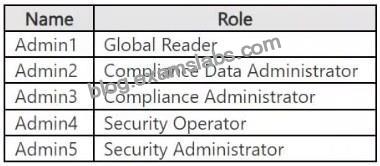
Q43. You have a Microsoft 365 E5 subscription that contains the users shown in the following table.

Which users will Microsoft Purview insider risk management flag as potential high-impact users?


Q44. You need to meet the technical requirements for the Site1 documents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

Q45. Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
You have a user named User1. Several users have full access to the mailbox of User1.
Some email messages sent to User1 appear to have been read and deleted before the user viewed them.
When you search the audit log in the Microsoft Purview portal to identify who signed in to the mailbox of User1, the results are blank.
You need to ensure that you can view future sign-ins to the mailbox of User1.
Solution: You run the Set-MailboxFolderPermission -Identity “User1” -User [email protected] -AccessRights Owner command.
Does that meet the goal?


Q46. You need to meet the technical requirements for the Site1 documents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

Q47. You have a Microsoft 365 ES subscription.
A security manager receives an email message every time a data loss prevention (DIP) policy match occurs.
You need to limit alert notifications to actionable DLP events. What should you do?


Q48. You have a Microsoft 36S ES subscription.
You need to create the Microsoft Purview insider risk management policies shown in the following table.

Which policy template should you use for each policy? To answer, drag the appropriate policy templates to the correct polices Each template may be used once more than once or not at all. You may need to drag the split bar between panes or scroll to view..

Q49. HOTSPOT
You have a Microsoft 365 E5 subscription that contains a user named User1.
You deploy Microsoft Purview Data Security Posture Management for AI (DSPM for AI).
You need to ensure that User1 can perform the following actions:
# View recommendations from the Recommendations page.
# View the user risk level for all events by using Activity explorer.
The solution must follow the principle of least privilege.
To which role group should you add User1 for each action? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q50. You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.

The subscription contains the resources shown in the following table.

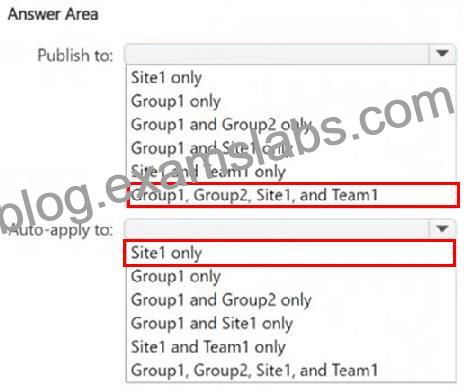
You create a sensitivity label named Label1.
You need to publish Label1 and have the label apply automatically.
To what can you publish Label1, and to what can Label1 be auto-applied? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.


The New SC-401 2025 Updated Verified Study Guides & Best Courses: https://www.examslabs.com/Microsoft/Microsoft-Certified-Information-Security-Administrator-Associate/best-SC-401-exam-dumps.html


Related Links: www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw fakescam.net www.stes.tyc.edu.tw